What it does
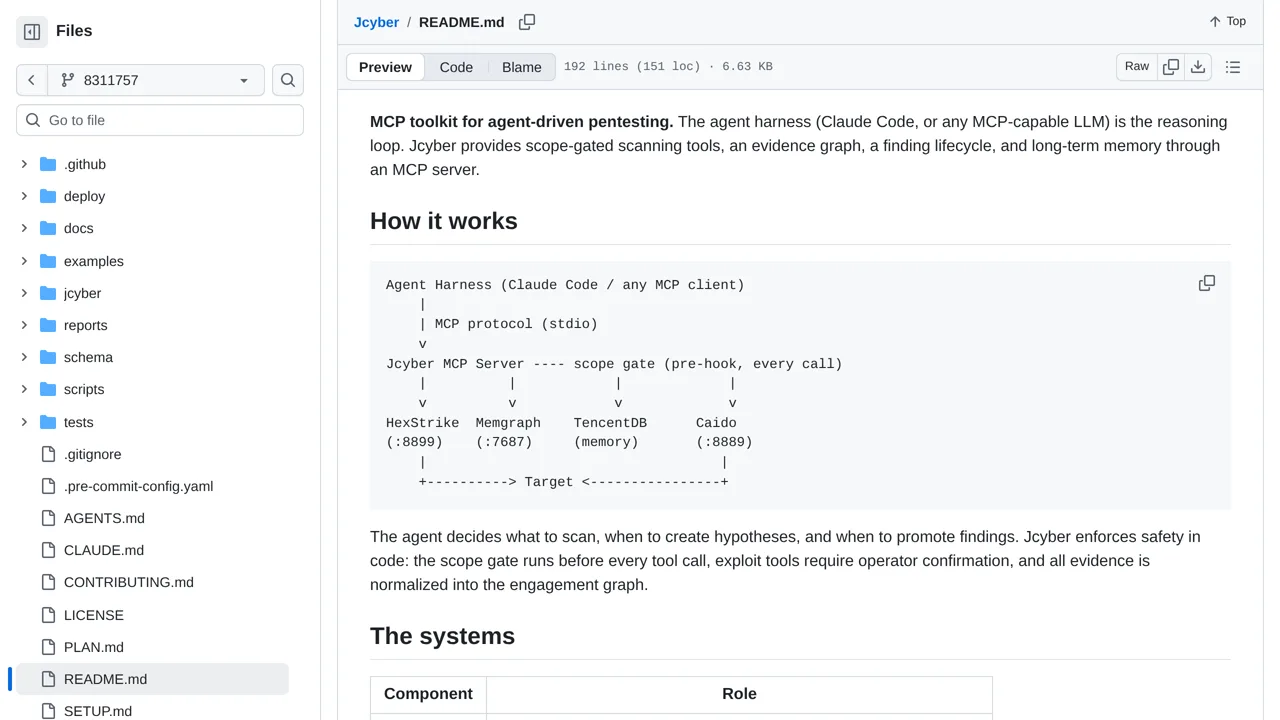
Adds fast severity and duplicate-evidence classifiers to a scope-gated MCP toolkit for agent-driven penetration testing.
Apps & data pipelines
Only you can see your notes.
Screenshot unavailable. Open the experiment ↗
Adds fast severity and duplicate-evidence classifiers to a scope-gated MCP toolkit for agent-driven penetration testing.
Use this record-keeping idea only on systems you own or have explicit permission to test. Start with Jcyber's Safety and Legality sections. Its checks for allowed systems do not grant permission or guarantee safe testing.
Save what each test found and where the evidence came from. Treat a possible problem as an idea to investigate, not a fact. Check that it is real before putting it in a report. A developer can borrow this process for your defensive testing records.