What it does
The numeric score follows the official equations; the uncertain part is choosing metric labels from incomplete vulnerability prose.
Apps & data pipelines
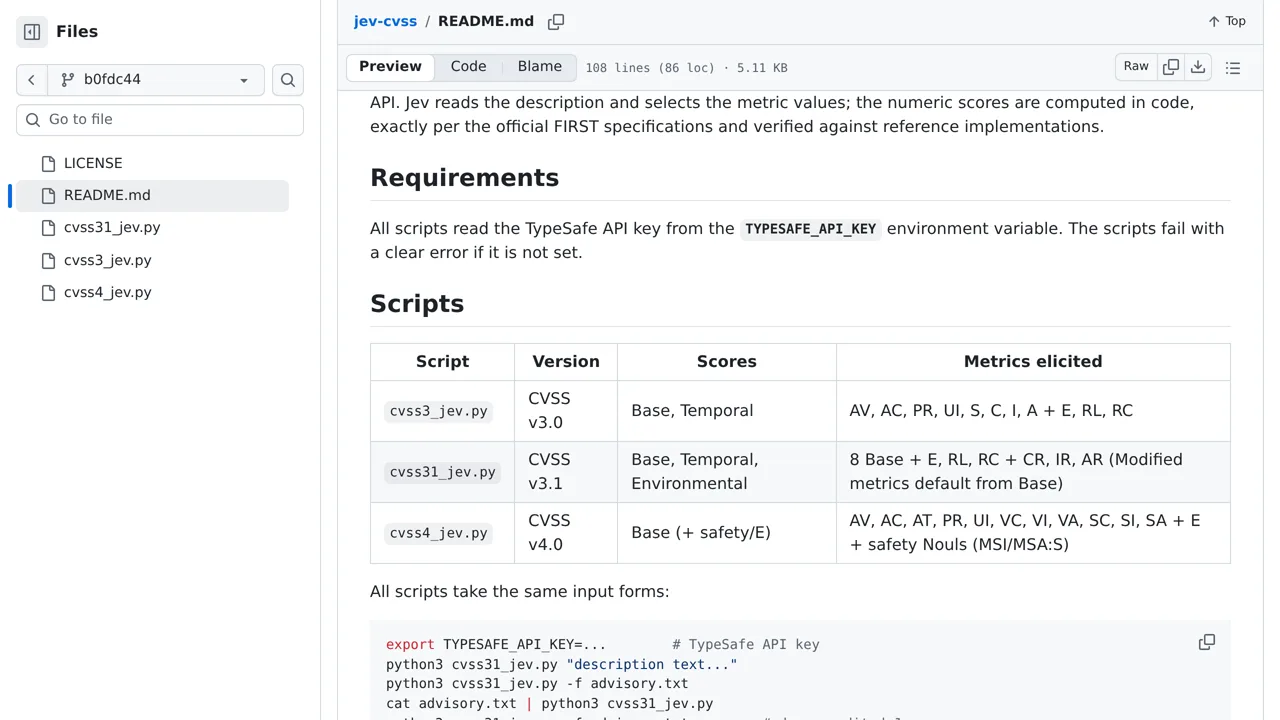
Maps vulnerability prose onto CVSS 3.0, 3.1 or 4.0 metrics, then calculates the official vector and score in Python.
Only you can see your notes.
Screenshot unavailable. Open the experiment ↗
The numeric score follows the official equations; the uncertain part is choosing metric labels from incomplete vulnerability prose.
Start by collecting written software bug reports that need security ratings. A developer can set up these scripts to inspect each report. To run the analysis, your developer must provide an access key from the TypeSafe online service.
The external service reads each bug write-up and chooses standard security labels. Next, the scripts use fixed math formulas to calculate an official severity score. Because incomplete bug descriptions can lead to wrong labels, a security specialist should still review important reports.