What it does
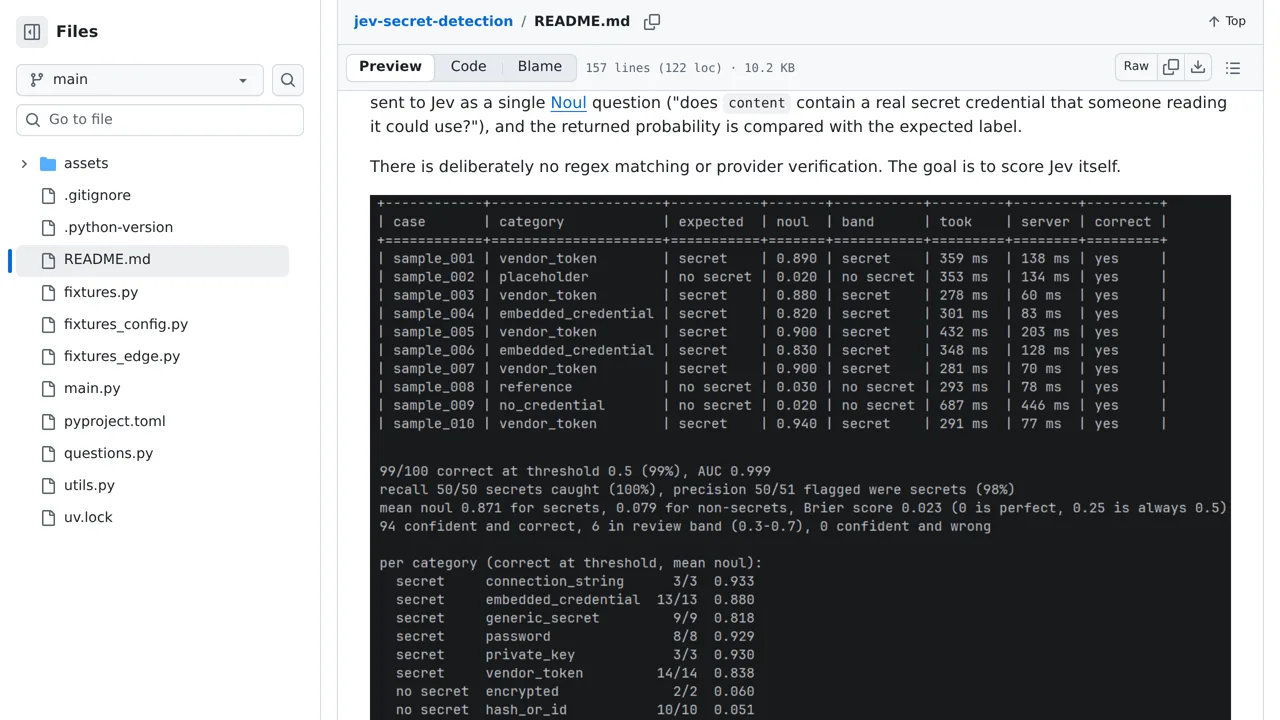
Can Jev tell a real credential from an innocent string? This benchmark tests it on file snippets.
Benchmarks & research
Screenshot unavailable. Open the experiment ↗
Can Jev tell a real credential from an innocent string? This benchmark tests it on file snippets.
Your developer can adapt this testing script to check your files for hidden passwords. The script reads short text snippets. It asks TypeSafe if those snippets contain real secrets instead of harmless test words. Your developer will need an access key from TypeSafe. This key connects your testing tool to their service.
The service takes time to read each snippet over the internet. Sending too many files at exactly the same time can overload the connection. The source script avoids this by testing files in small groups. Your developer can borrow this approach to keep the tests running smoothly.