What it does
The model judges incident relatedness, not whether a process is malware. Missing telemetry links limit what it can find, and results need analyst review, especially near the decision threshold.
Apps & data pipelines
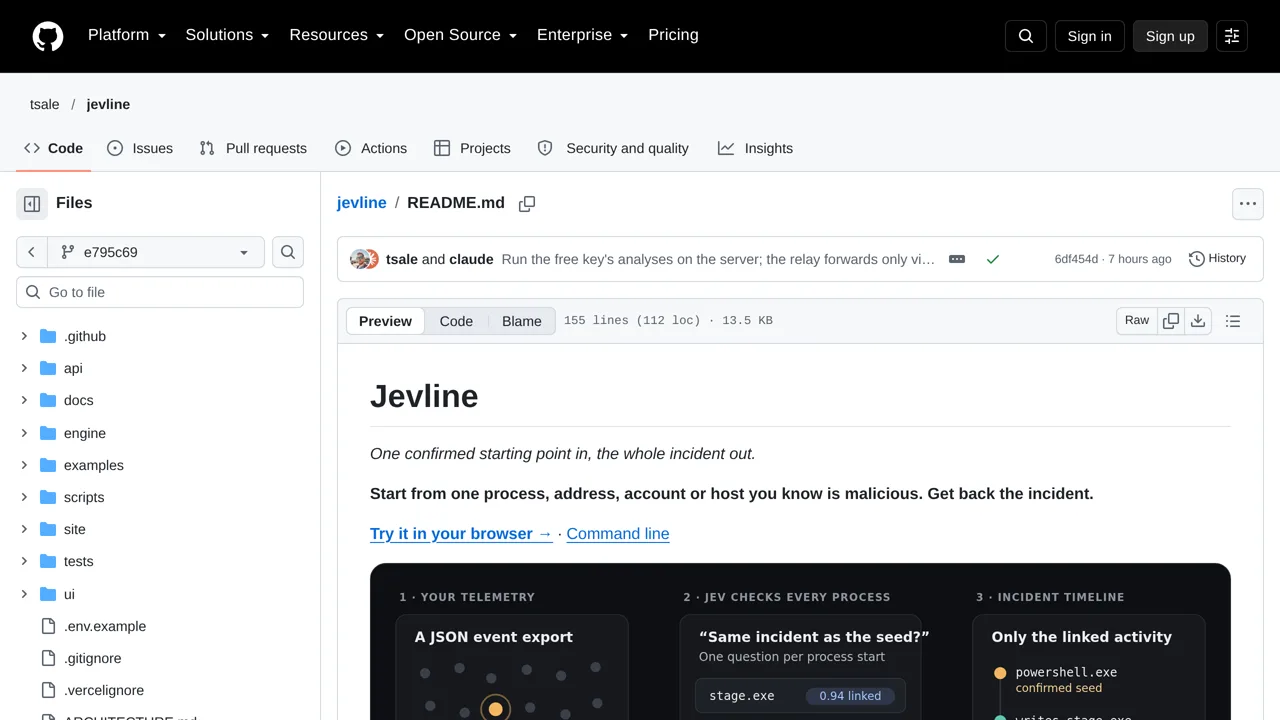
Start from one confirmed malicious process or account, then let Jev follow recorded links to build an incident timeline.
Only you can see your notes.
Screenshot unavailable. Open the experiment ↗
The model judges incident relatedness, not whether a process is malware. Missing telemetry links limit what it can find, and results need analyst review, especially near the decision threshold.
Try the bundled example first. You choose one program already known to be involved in an attack, and Jev decides which connected actions belong to the same incident. A security analyst must review the results. Before trying your own records, check that you are allowed to share them with the outside AI service.