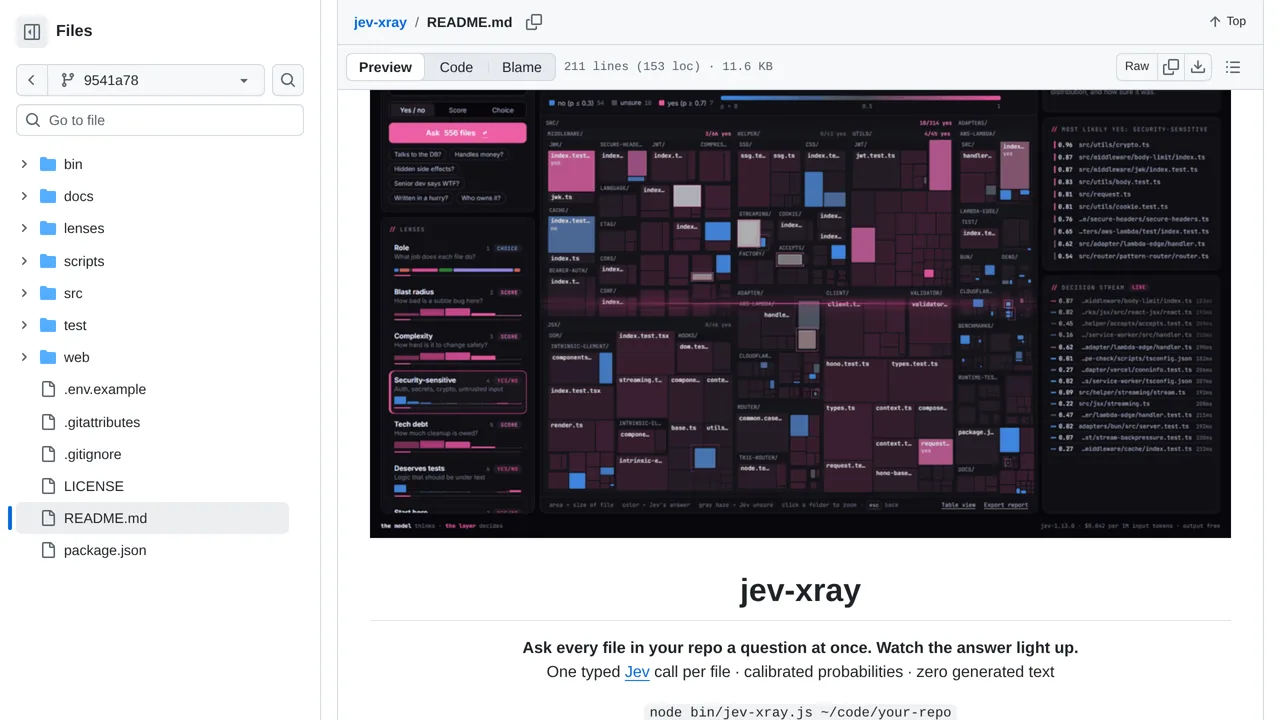
File excerpts leave your machine for TypeSafe; large files use only their start and end. Saved content hashes avoid repeat calls, and a labelled simulation mode needs no API calls. Risk labels are investigation aids, not proof that code is safe.
How you can use it
Ask a developer to use this map when exploring an unfamiliar software project. Its views can suggest files to read for a feature, a complex change or a possible security concern. Read the highlighted code yourself; the tool’s guess is a starting point for investigation, not a confirmed finding.
The tool sends parts of your code to TypeSafe, the company providing Jev, so share only code your team is allowed to disclose. Very large files lose their middle sections. A clearly marked practice mode shows the interface without sending code to the AI service. Saved checks avoid repeat charges for unchanged files.